How to Choose an AI Agent Development Company in 2026 is designed for teams moving from AI experimentation to a governed business capability. The useful question is not whether a model can produce an impressive answer. It is whether a system can complete a defined job, use approved data and tools, stop at the right boundary, recover from failure, and leave evidence that people can audit.
This guide takes a buyer-focused evaluation guide that helps an enterprise shortlist a partner without duplicating a service-page pitch. It separates proven engineering patterns from marketing shorthand and gives buyers, product leaders and technical teams a shared way to make decisions.
Quick answer: A reliable ai agent development company initiative starts with one bounded workflow, explicit success and failure criteria, narrow permissions, representative evaluation cases, human control over consequential actions, and a measured rollout. Model selection matters, but the surrounding software and operating controls usually determine whether the agent survives production.
What readers should take away
- How to evaluate ai agent development company without confusing a prototype with a production system
- Which architecture and operating controls matter most
- How to define a safe first release and measurable acceptance criteria
- Where DreamzTech services, solutions and implementation evidence can support the next step
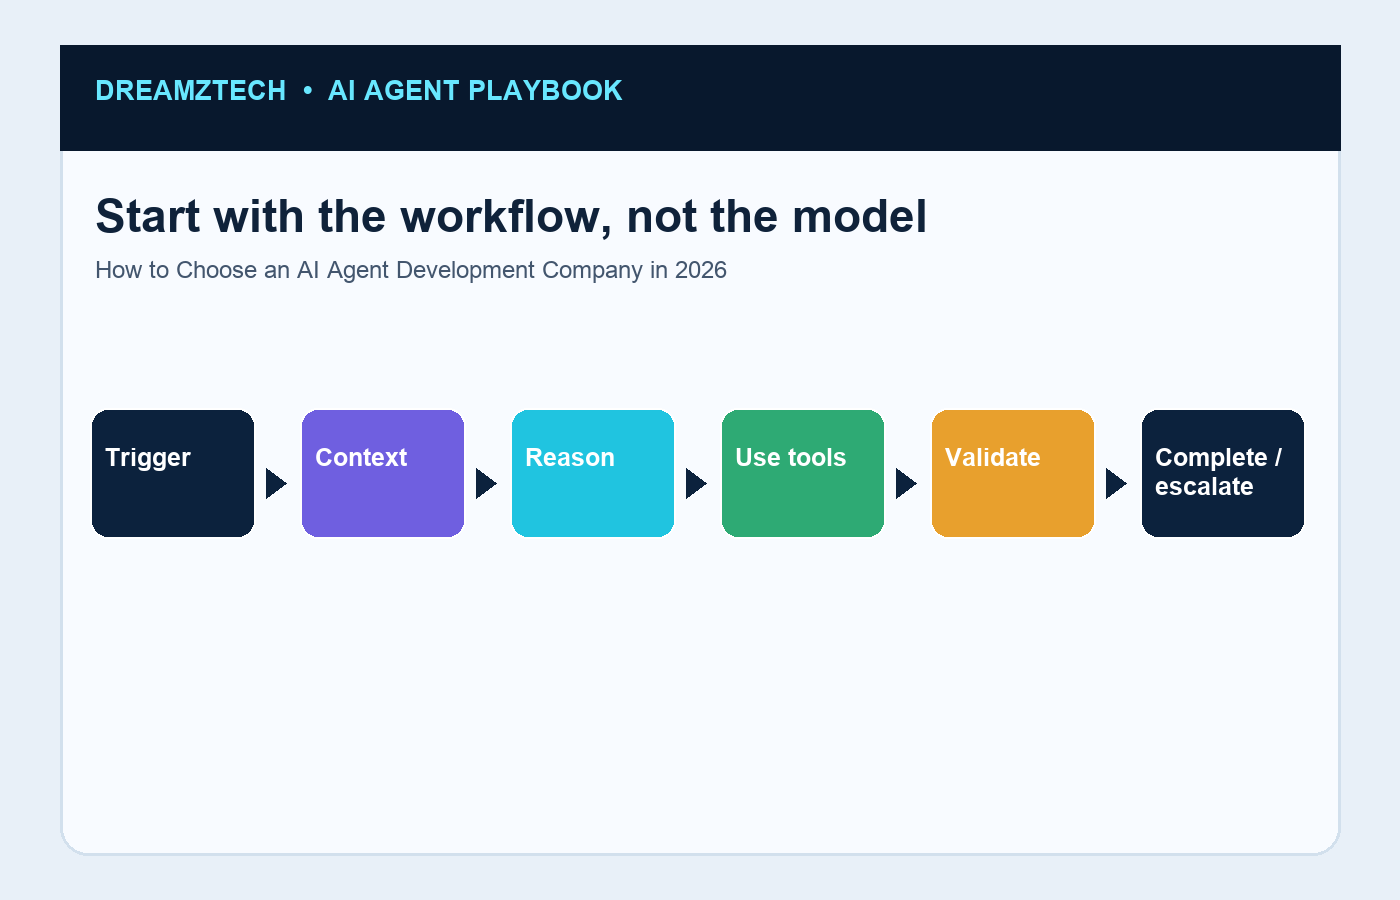
Start with the workflow, not the model
Start by naming the actor, trigger, inputs, systems of record, permitted actions and completion condition. If the team cannot draw the workflow and identify its owner, an agent will inherit that ambiguity. The first design artefact should therefore be an operational boundary, not a prompt.
Ground the agent in the minimum context needed for the task. Retrieval should respect the requesting user's entitlements, cite the underlying record where practical, and abstain when evidence is incomplete. More context is not automatically better context.
- Define a named owner and measurable completion condition
- Limit tools and data to the minimum required
- Add explicit exception, escalation and recovery paths
- Test with representative and adversarial scenarios
12 capabilities a production partner must prove
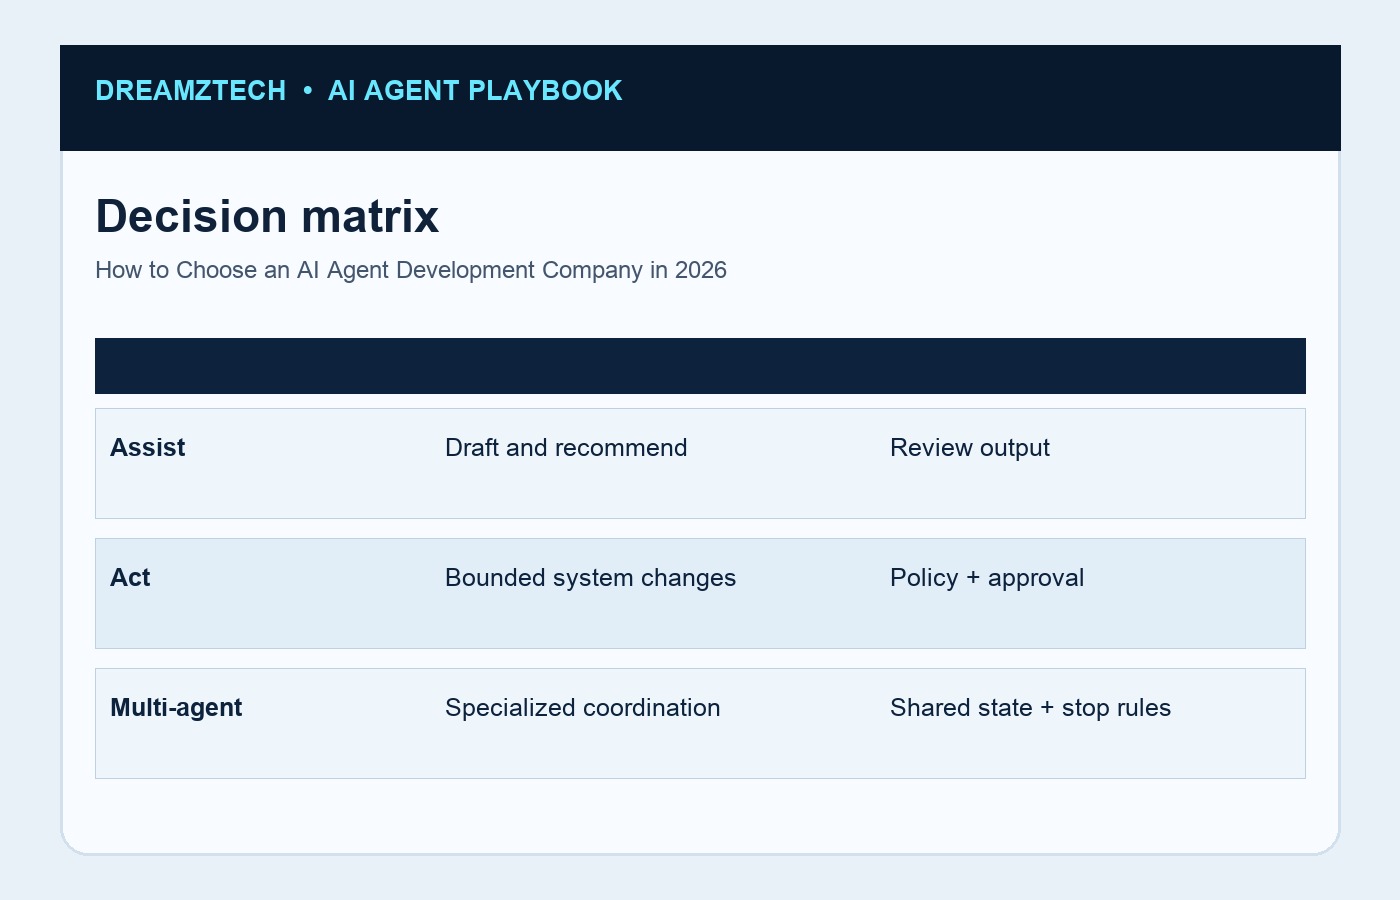
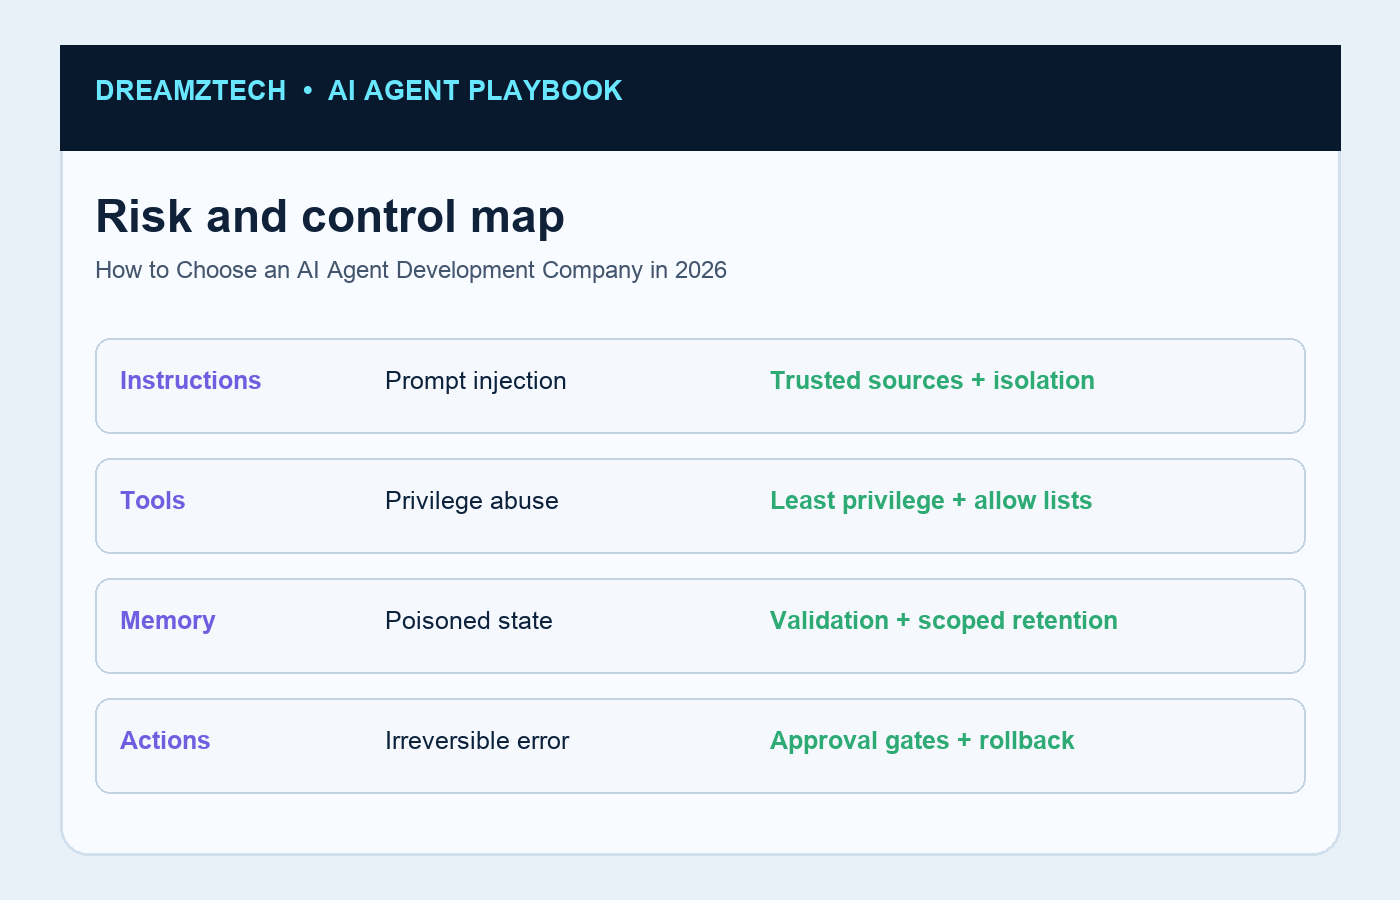
Separate deterministic business rules from model judgement. Validation, permissions, monetary limits, routing rules and irreversible actions belong in explicit software controls. The model can interpret messy input and select among allowed tools, but it should not invent its own authority.
Evaluate complete trajectories rather than final prose. A successful run uses the right data, chooses the right tool, handles partial failure, requests approval when required and stops when the job is complete. Scenario suites should include normal cases, edge cases, malicious inputs and dependency outages.
- Define a named owner and measurable completion condition
- Limit tools and data to the minimum required
- Add explicit exception, escalation and recovery paths
- Test with representative and adversarial scenarios
How to evaluate architecture, security and integrations
Treat every tool as a contract. Define accepted inputs, returned outputs, timeouts, idempotency behaviour, error classes and the credentials required. Narrow tools make an agent easier to test, easier to revoke and much easier to explain during a security review.
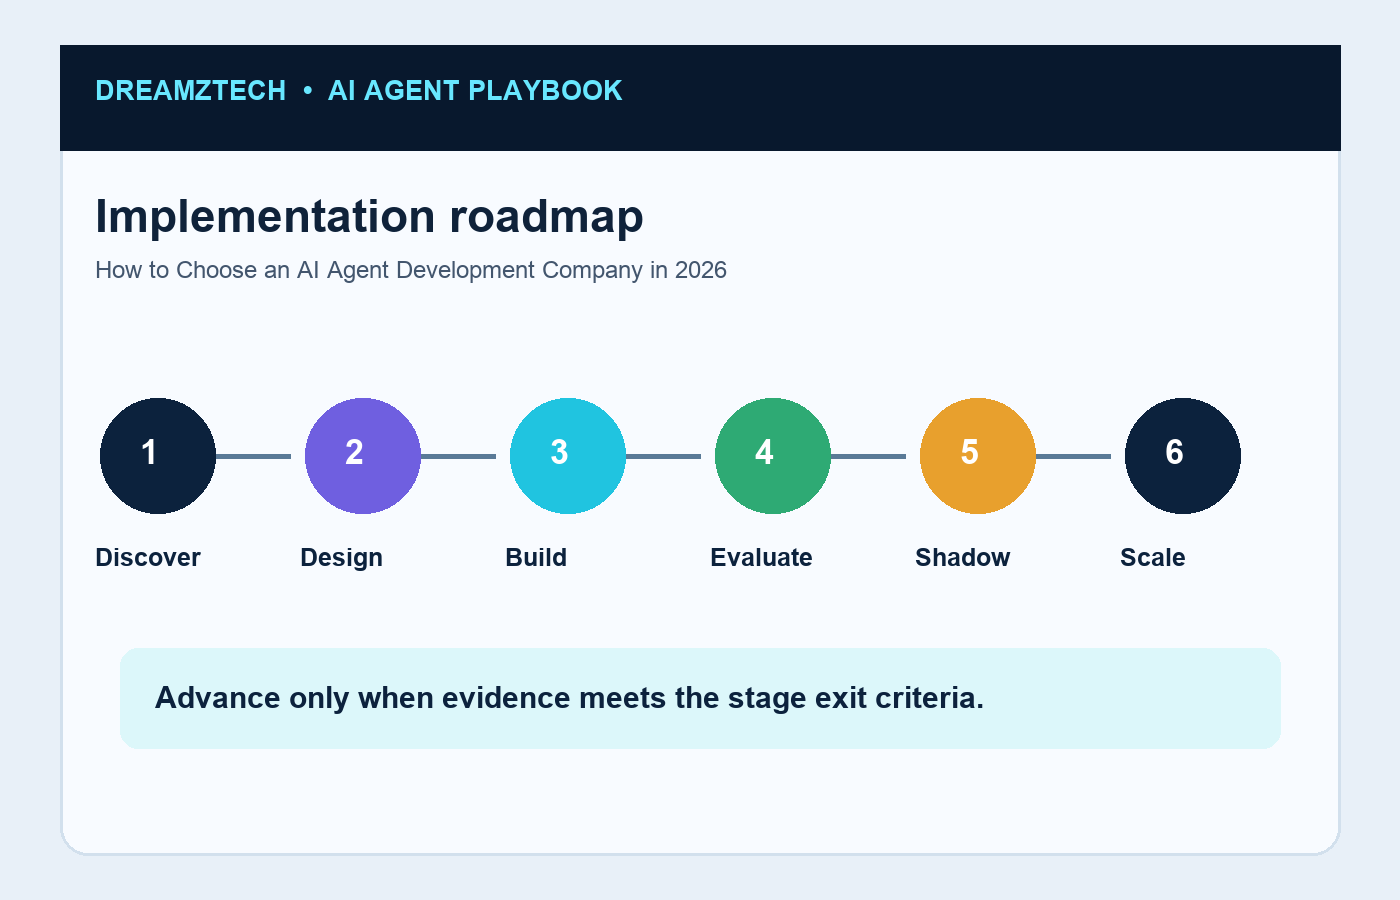
Release in stages: offline evaluation, a sandbox connected to test systems, shadow mode in which the agent proposes without acting, a narrow live slice, and only then broader authority. Each stage needs an owner, exit criteria, a tested disable path and a rollback plan.
- Define a named owner and measurable completion condition
- Limit tools and data to the minimum required
- Add explicit exception, escalation and recovery paths
- Test with representative and adversarial scenarios
Questions to ask during vendor discovery
Ground the agent in the minimum context needed for the task. Retrieval should respect the requesting user's entitlements, cite the underlying record where practical, and abstain when evidence is incomplete. More context is not automatically better context.
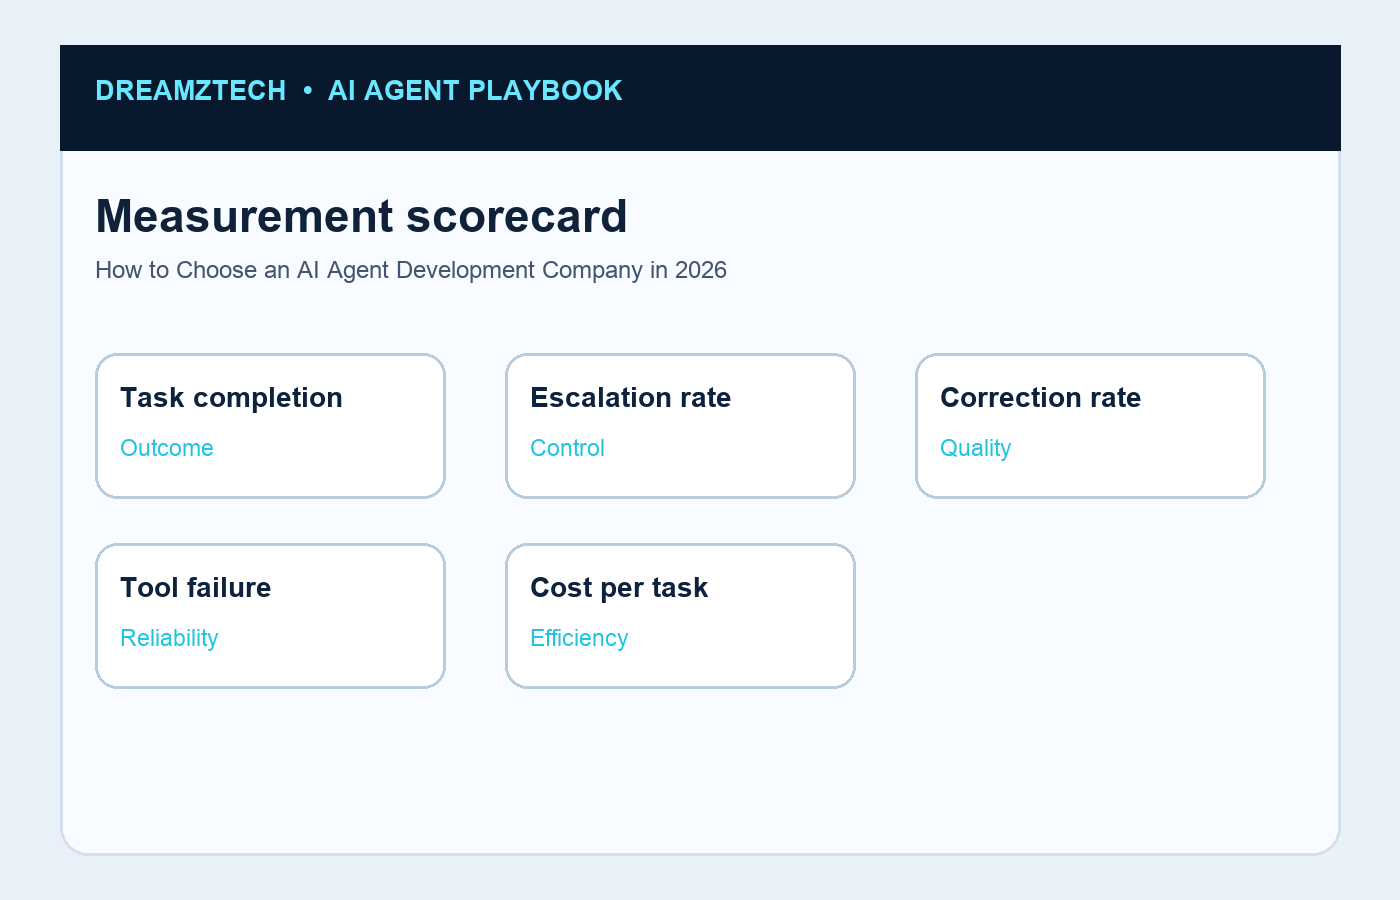
Measure task outcomes, not token activity. Useful metrics include completion rate, escalation rate, correction rate, tool-call failure rate, latency, cost per completed task, policy violations and business impact. Review the failures behind the averages because they reveal where controls or workflow design need attention.
- Define a named owner and measurable completion condition
- Limit tools and data to the minimum required
- Add explicit exception, escalation and recovery paths
- Test with representative and adversarial scenarios
Red flags in AI agent proposals
Evaluate complete trajectories rather than final prose. A successful run uses the right data, chooses the right tool, handles partial failure, requests approval when required and stops when the job is complete. Scenario suites should include normal cases, edge cases, malicious inputs and dependency outages.
Ownership continues after launch. Business operations owns the outcome and policy; engineering owns reliability and integration; security owns control requirements; and a named product owner decides what changes. Models, prompts, APIs and source data drift, so evaluation and review must be continuous.
- Define a named owner and measurable completion condition
- Limit tools and data to the minimum required
- Add explicit exception, escalation and recovery paths
- Test with representative and adversarial scenarios
A weighted shortlist scorecard
Release in stages: offline evaluation, a sandbox connected to test systems, shadow mode in which the agent proposes without acting, a narrow live slice, and only then broader authority. Each stage needs an owner, exit criteria, a tested disable path and a rollback plan.
Start by naming the actor, trigger, inputs, systems of record, permitted actions and completion condition. If the team cannot draw the workflow and identify its owner, an agent will inherit that ambiguity. The first design artefact should therefore be an operational boundary, not a prompt.
- Define a named owner and measurable completion condition
- Limit tools and data to the minimum required
- Add explicit exception, escalation and recovery paths
- Test with representative and adversarial scenarios
From proof of concept to production
Measure task outcomes, not token activity. Useful metrics include completion rate, escalation rate, correction rate, tool-call failure rate, latency, cost per completed task, policy violations and business impact. Review the failures behind the averages because they reveal where controls or workflow design need attention.
Separate deterministic business rules from model judgement. Validation, permissions, monetary limits, routing rules and irreversible actions belong in explicit software controls. The model can interpret messy input and select among allowed tools, but it should not invent its own authority.
- Define a named owner and measurable completion condition
- Limit tools and data to the minimum required
- Add explicit exception, escalation and recovery paths
- Test with representative and adversarial scenarios
Recommended next step
Use this guide to create a one-page scope, then compare it with DreamzTech’s AI agent development company, custom AI agent development services, AI agent consulting. The purpose of these links is to move a reader from education to the most relevant service or proof page without making this article compete with the commercial landing page.
Turn one workflow into a production plan
Bring one workflow and its constraints to a 30-minute architecture discussion.
Frequently asked questions
What does an AI agent development company do?
A useful answer depends on workflow scope, action authority, data sensitivity, integrations and acceptance criteria. Start with a bounded task, narrow permissions, representative tests and a clear human escalation path; expand only when evidence supports it.
Which companies can develop custom AI agents for an enterprise?
A useful answer depends on workflow scope, action authority, data sensitivity, integrations and acceptance criteria. Start with a bounded task, narrow permissions, representative tests and a clear human escalation path; expand only when evidence supports it.
How do I compare AI agent vendors?
A useful answer depends on workflow scope, action authority, data sensitivity, integrations and acceptance criteria. Start with a bounded task, narrow permissions, representative tests and a clear human escalation path; expand only when evidence supports it.
How long should an enterprise AI agent pilot take?
A useful answer depends on workflow scope, action authority, data sensitivity, integrations and acceptance criteria. Start with a bounded task, narrow permissions, representative tests and a clear human escalation path; expand only when evidence supports it.
What should an AI agent proposal include?
A useful answer depends on workflow scope, action authority, data sensitivity, integrations and acceptance criteria. Start with a bounded task, narrow permissions, representative tests and a clear human escalation path; expand only when evidence supports it.
Editorial note: This article provides general technology and implementation guidance, not legal, medical or compliance advice. Requirements should be validated for the organization, jurisdiction and use case.